Perimeter & network
Firewall, segmentation, IDS/IPS and secure remote connection of your sites
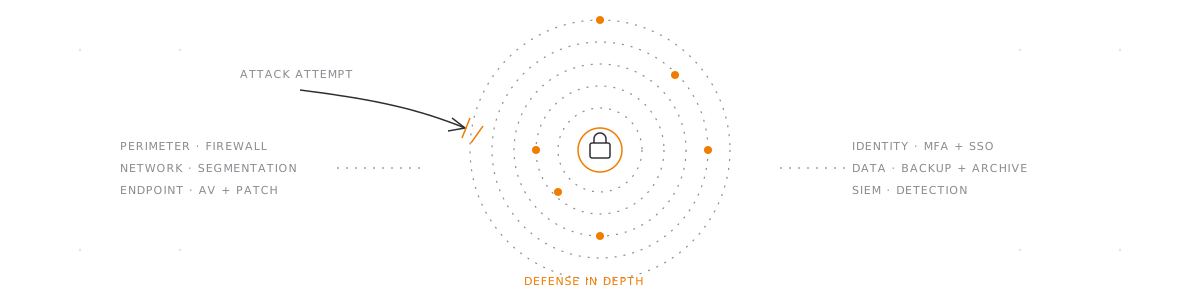
OPNsense / NetBirdIT security is built from several levels of protection, from the firewall at the edge of your network to the awareness of your staff. We work with clear measures, documented tests and a plan for emergencies.
Firewall, segmentation, IDS/IPS and secure remote connection of your sites
OPNsense / NetBirdManaged antivirus, application control and disk encryption on every device
Defender / BitLockerSingle sign-on, multi-factor authentication and a strict least-privilege model
Zitadel SSOMulti-stage filtering against phishing, spam, malware and business email compromise
Mailcow ASSPEncrypted, monitored backups as the last line of defence against ransomware, optionally also in a second data centre
Proxmox PBS / BaculaRegular training, phishing simulations and a documented training history
Lucy / Sosafe→ No single measure is certain to stop a determined attacker. Six lines of defence in a row make it much harder. That is defence in depth.
Configuration, patching and monitoring of your OPNsense firewalls. Clean rule sets, documented, versioned and reviewed.
Centrally managed protection for your devices. We monitor in real time and report suspicious activity automatically.
Managed Backup via Proxmox Backup Server or Bacula in data centres in Germany. Backup in a second data centre and documented restore tests as options, emergency plan charged by effort.
Protection against phishing, spam and malware through multi-stage filtering, DKIM/SPF/DMARC and continuous reputation checks.
Periodic scans of your infrastructure, prioritised by CVSS and contextual risk assessment. Fixes go through our change management.
We provide quarterly training, phishing simulations and individual reports.
We analyse your security status against the BSI IT-Grundschutz modules and identify the critical gaps.
A prioritised roadmap with quick improvements and medium-term measures. For each step we state the effort and the benefit.
We put the measures in place, from firewall rules to setting up Conditional Access.
Security needs ongoing care. We look after the set-up continuously, train your team and review the risks every quarter.
One account for all your applications. We run Zitadel as an identity provider ourselves, based on the OIDC standard and with MFA mandatory from the start.
We back up your physical and virtual servers with Acronis Cyber Protect. Each backup captures the whole server as an image, handles running applications consistently and is held in cloud storage in Germany.
We back up notebooks and desktop PCs with Acronis Cyber Protect. Each backup is an image of the whole device (block-level image), stored in a data centre in Germany. You can restore single files or the entire device.
We check your IT against GDPR and ISO standards on an ongoing basis. The technical controls run automatically, and you receive a report every quarter.
We manage the antivirus protection on your workstations and servers centrally. As standard we use Microsoft Defender Antivirus (built into Windows), controlled through our RMM; a third-party product is also possible. Alerts go to the service desk, and you receive a report on protection coverage weekly (recommended) or at an interval of your choice.
A firewall for your site based on OPNsense. This open-source solution offers the features of large commercial products, and Netsource looks after it and installs the updates.
Every member of staff signs in with a second factor (multi-factor authentication, MFA) using a TOTP app, a FIDO2 security key or a passkey. Zitadel enforces this centrally.
Detection of and response to attacks on workstations and servers (endpoint detection and response). We enable the standard policies, and the Netsource service desk reviews the alerts.
We install updates on workstations and servers in an orderly way: first in a test group, then on all devices, without restarts at awkward moments. Each month you receive a report on the current status.
We collect and assess security events from your devices, servers and cloud services in one place. We run the platform and read the alerts, and critical incidents reach you as tickets.
In a two-hour assessment we find the critical gaps before an attacker does. You receive the findings in writing.